Blog Post
When a cloud incident hits, every minute counts.
At Field Effect, we’ve made it our mission is to stop attacks as early as possible, before threats can spread and cause real damage. Using behavioral analytics and the full context of each user, Field Effect separates expected activity from malicious behavior. Then you receive only the alerts that matter, no noise or distraction.
But stopping the threat isn’t always the end of the story. Sometimes you need to walk a client or stakeholder through the attack step by step or see the exact indicators of compromise (IOCs) that led our experts to deem it malicious.
That’s where Field Effect’s Cloud Investigation Reports come in. They tell the full story, so you can validate the verdict and explain it with confidence.
Cloud Investigation Reports provide the clarity and context of what happened during an incident, with the flexibility to either review how the attack unfolded at a high level or drill down to analyze and investigate the raw data yourself.
These reports share all the data our analysts use to investigate incidents (timeline, historical context, and evidence) so you can answer questions such as:
What tactics did the attacker use to compromise the account?
Why did Field Effect determine certain activity malicious or benign?
Did the attacker configure persistence?
What emails did the attacker access once inside?
Was there any other malicious activity that happened around the time of the incident?
What actions have been taken and what should I do now?
For every investigation, Field Effect reconstructs a timeline of all suspicious activity, including the IOCs and contextual signals that guided our analysts.
You'll be able to view any alerts, known as AROs, that were issued, such as:
Suspicious sign-ins from unrecognized locations, devices, or VPNs
Suspicious user authentications
Suspicious changes to inbox rules
The report also includes any alerts that were not issued, typically to minimize noise, including:
Accessed or deleted mail and files
Consent granted to applications
Registered new devices or authentication methods
And more
Every step lets you drill into the evidence behind each finding and the entities it affected, with the raw data at your fingertips so you can verify malicious activity and understand the context of each finding.
You can also review the remediation actions Field Effect has already taken, and any that are still outstanding, so you can confirm every sign of the attack has been cleaned up.
If you want to understand why an activity is suspicious for a specific account, the Account snapshot gives you that context without having to leave the report.
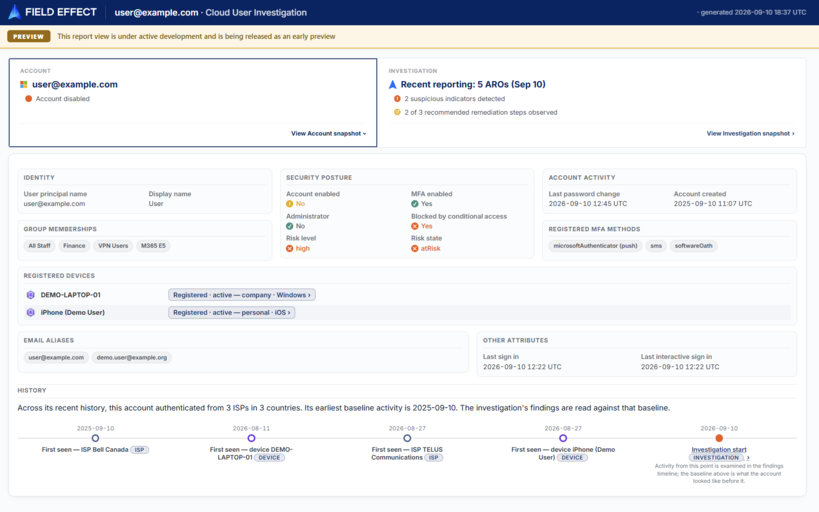 For Microsoft 365 accounts, you can review the account's identity details, email, group memberships, registered devices, and time of last password change, along with security settings like administrator status, risk level, and MFA status. The report also outlines historical context, showing what normal behavior looked like for that user prior to the investigation, all in one place.
That baseline, along with how it compares to other users across the organization, is the standard against which suspicious activity is measured. This produces high-fidelity detections and makes it easy to see why activity was flagged and where a threat actor’s behavior differs from the norm.
Want to know exactly what the attacker did once inside the cloud account? The User Activity tab has the answer, with every log for you to search.
From here you can review all user activity and filter logs by ISP or suspected malicious session, then dig into exactly what happened during it:
Accessed or sent mail items
Failed and successful sign-ins
File downloads
Changed inbox rules
Registered devices
Consent granted to third-party applications
Field Effect already highlights the log entries most likely tied to the incident, so you know where to look first. But you're not limited to those; you can also explore the surrounding activity, drill into the raw event data behind any entry, and export what you find for your own reporting.
Whether you're confirming a single suspicious sign-in or piecing together everything an attacker touched during a compromise, Cloud Investigation Reports start you off the same way: clear insights and forensic-level depth that answer any question you have.
You can stay high level or go as granular as needed for the situation at hand. Either way, you have what you need to explain what happened during the incident and demonstrate value during the investigation process.
Cloud Investigation Reports are now available in the Field Effect portal for all Microsoft 365 cloud investigations.